Home / Services / IT Compliance & NIS2 Readiness
Security & Compliance
NIS2 & GDPR Compliance, Made Practical
Audit-ready documentation and evidence for NIS2, GDPR and the AI Act, in plain English.
Compliance Has Become Unavoidable, and Most SMEs Are Not Ready
The EU NIS2 Directive significantly widens who is covered by cybersecurity regulation. Penalties for essential entities can reach €10 million or 2% of global turnover. Beyond NIS2, you face:
- GDPR data protection requirements
- Growing expectations from larger customers around security posture
- Industry-specific requirements depending on your sector
Most SMEs have no idea where to start. The frameworks look impenetrable.
Worth reading first: does NIS2 apply to your business, and what the DPC’s recent €403m Google fine means for the GDPR side of the picture.
Our solution
Practical, Step-by-Step Compliance
We assess where you stand against the frameworks that apply to you, fix the gaps, and document everything properly so you can face an audit with confidence.
Included
What’s Included
Included in every tier
- Compliance gap assessment (NIS2, GDPR, AI Act)
- Control register and compliance dashboard
- Plain-English documentation, no regulatory jargon
- Risk register and remediation plan
- Evidence trail suitable for audits and insurance
Fit
Who It’s For
This service is a good fit for:
- SMEs unsure whether NIS2 applies to them
- Businesses supplying larger regulated organisations
- Companies in transport, energy, digital infrastructure, or healthcare
- Businesses that need audit-ready evidence for customers or insurers
Often combined with our cybersecurity and network security service to cover both the paperwork and the technical controls behind it.
Process
How It Works
01. Gap Audit
Full assessment against NIS2/GDPR requirements, prioritised remediation plan. Typically 2-3 weeks.
02. Remediation
We work through the plan with you: policy, technical controls, documentation.
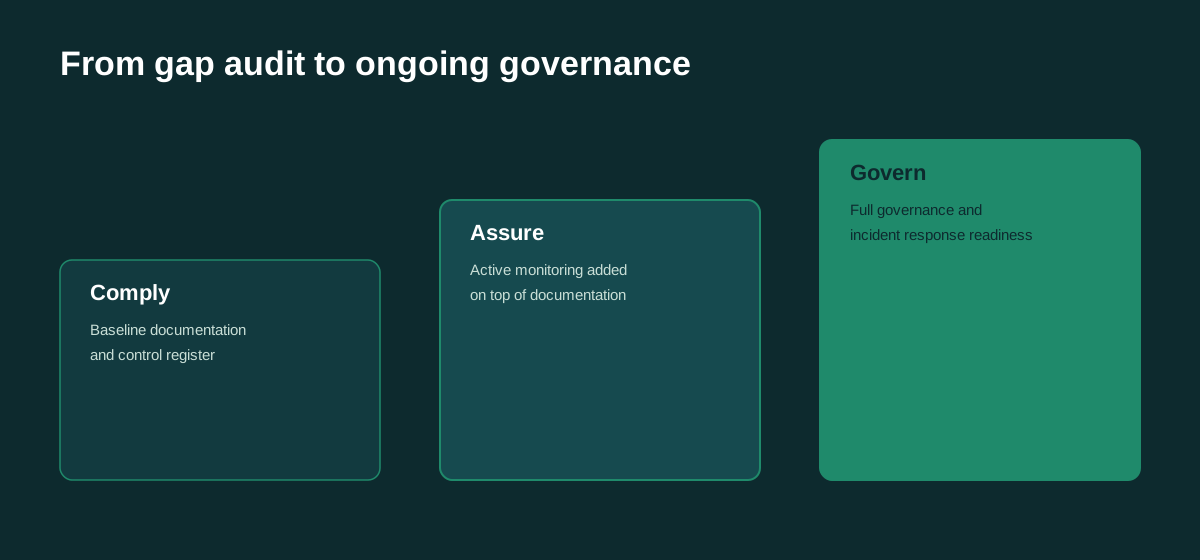
03. Ongoing tier
Move into Comply, Assure, or Govern for continued monitoring.
Pricing
Pricing & Timeline
Gap Audit €1,950 one-off, credited against your first three months if you continue. Ongoing tiers: Comply €395/month, Assure €850/month, Govern €1,650/month.
FAQ
Common Questions
Do I need to be NIS2 compliant?
Many Irish SMEs that supply larger regulated organisations may be in scope. A short exposure check is the fastest way to know.
What is the difference between the tiers?
Comply covers baseline documentation. Assure adds active monitoring. Govern adds full governance and incident response readiness.
Is Your Business NIS2-Ready?
Find out where you stand, free IT audit and NIS2 exposure check.